 DE

Important facts about NIS 2
- What is NIS2?
- NIS2 is an EU directive that requires companies in critical and important sectors to implement structured cyber risk management and to report serious security incidents.
- Since when has NIS2 been in effect in Germany?
- The German NIS2 Implementation Act entered into force on December 6, 2025, without a transition period.
- Who is affected by the NIS 2 Directive?
- This affects companies in 18 sectors with 50 or more employees or annual revenue of more than 10 million euros, as well as, indirectly, their suppliers and IT service providers.
- What are the obligations of affected companies?
- They must implement ten security measures, including securing their supply chain, registering with the BSI, and reporting significant incidents within 24 hours of their occurrence.
- What are the consequences of violations?
- Fines of up to 10 million euros or 2 percent of global revenue may be imposed, and management is personally liable.
Abstract
The NIS 2 Directive significantly expands the scope of regulated companies. Previously, approximately 4,500 KRITIS organizations were subject to BSI oversight; now there are about 29,500 companies. Among them are many small and medium-sized enterprises in the manufacturing, chemical, food, and logistics sectors that had not previously considered themselves to be critical infrastructure.
Essentially, the law requires a risk management system that can be proven to work. This includes ten areas of action, a reporting process that ensures an initial report is filed within 24 hours, and registration with the BSI. Management bears personal responsibility for this.
The supply chain is the most commonly underestimated factor. Cloud providers, IT service providers, and maintenance partners must be identified, bound by contract, and continuously monitored. Even organizations that are not subject to NIS2 themselves will still feel the impact of the law through their customers’ contracts, questionnaires, and documentation requirements.
Even those who are not themselves subject to the NIS2 Directive are often indirectly affected. Customers subject to NIS2 pass their security requirements on to suppliers and service providers through contracts.
Never miss an update on the LkSG again.
New specialist articles, regulatory updates and practical tips, straight to your inbox. Once a week, no spam.
What is NIS2?
The NIS2 Directive is the EU’s central regulatory framework for cybersecurity. It requires companies in critical and important sectors to systematically manage cyber risks, implement appropriate protective measures, and report serious security incidents in a timely manner. Its official name is Directive (EU) 2022/2555; the abbreviation stands for “Network and Information Security.”
As a directive, NIS-2 is not directly applicable; rather, it must be transposed into national law by each EU member state. For this reason, details such as the relevant authorities, portals, and terminology vary from country to country. What the EU refers to as “critical infrastructure” is called “particularly important infrastructure” in Germany.
What's new compared to NIS1?
The NIS2 Implementation Act is a further development of the first NIS Directive from 2016. That directive primarily applied to traditional operators of critical services and a small number of digital service providers. Since then, cyberattacks have become more sophisticated and no longer target only operators of critical infrastructure, but increasingly affect companies through their digital dependencies: cloud services, remote maintenance, and software updates.
NIS2 responds to this with four key changes:
- Broader scope of application: 18 sectors instead of 7, and a fixed size threshold. As a result, many medium-sized companies are affected for the first time.
- Specific minimum measures: A fixed set of requirements leaves auditors less room for interpretation.
- The Supply Chain as a Requirement: Ensuring secure relationships with service providers is an explicit part of risk management.
- Management's Liability: Management is personally liable, subject to EU-wide harmonized fines.
How is NIS2 being implemented in Germany?
Germany is implementing NIS2 through the NIS2 Implementation and Cybersecurity Strengthening Act, or NIS2UmsuCG for short. This is not a standalone “NIS2 Act,” but primarily a revised version of the BSI Act (BSIG). Anyone looking for the specific obligations will therefore find them in the BSIG.
The NIS2 requirements are not set forth in the implementing act itself, but rather in the revised BSI Act (BSIG).
From an EU Decision to German Law
The NIS2 Directive took effect throughout the EU on January 16, 2023. Member states were required to implement it by October 17, 2024. Germany missed this deadline by a wide margin: The first draft bill failed due to the collapse of the “traffic light” coalition, and the European Commission launched infringement proceedings in November 2024, which it escalated in May 2025.
The bill didn't pass until the second attempt. Here's an overview of the key milestones:
- November 13, 2025: The Bundestag passes the NIS2 Implementation Act.
- November 20, 2025: The Federal Council approves the law.
- December 6, 2025: The law takes effect without a transition period.
- January 6, 2026: The BSI opens its registration portal.
- March 6, 2026: The statutory registration deadline expires.
- July 31, 2026: The grace period granted by the BSI expires.
Which sections of the law should you be familiar with?
In practice, the following provisions of the BSIG are particularly important:
- § 28 BSIG: Who Is Considered a Particularly Important or Important Institution
- § 30 BSIG: the ten risk management measures, including supply chain security
- § 32 BSIG: The Three-Tier Reporting Requirement
- § 33 BSIG: Registration with the BSI
- § 38 BSIG: Duties and Liability of Management
- Sections 61 and 62 of the BSIG: Supervision by the BSI
- § 65 BSIG: Fines
NIS2: Who Is Affected?
Whether a company falls under NIS2 depends on three factors: the sector, the company’s size, and any special circumstances. Companies operating in one of the 18 sectors that are classified as at least medium-sized are generally directly affected.
Which sectors does NIS2 cover?
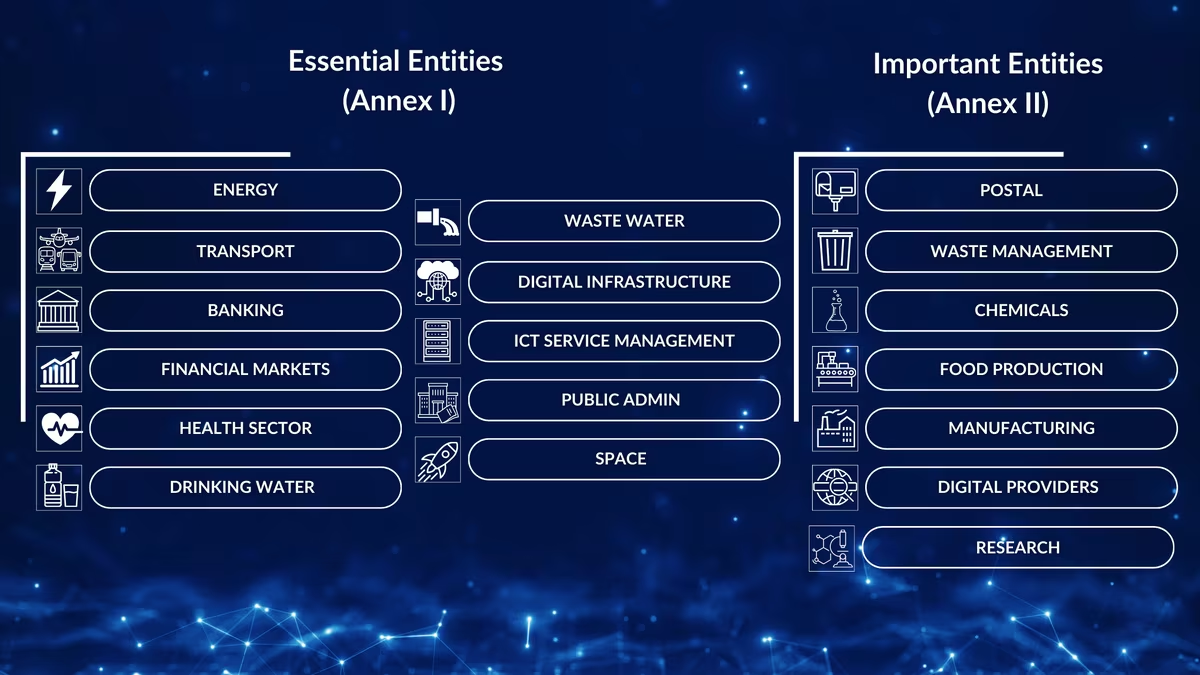
The law distinguishes between two groups of sectors.
High-criticality sectors:
- Energy
- Transportation and Traffic
- Banking and Financial Market Infrastructures
- Health
- Drinking Water and Wastewater
- Digital infrastructure, such as cloud providers and data centers
- ICT Service Management, particularly Managed Service Providers
- Public Administration
- Space
Other critical sectors:
- Postal and Courier Services
- Waste Management
- Chemistry
- Food
- Manufacturing industry, ranging from mechanical engineering to electronics and automotive manufacturing
- Digital services such as online marketplaces and search engines
- Research
At what size does NIS2 apply?
Classification is based on the number of employees, revenue, and total assets:
- Major organization: at least 50 employees or more than 10 million euros in annual revenue and total assets
- Particularly important organization: at least 250 employees or more than 50 million euros in revenue and more than 43 million euros in total assets, in a sector with a high level of criticality in each case
Affiliated companies are generally included in this calculation. A small subsidiary may therefore be affected even though it falls below the thresholds on its own.
NIS2 generally applies to companies with 50 or more employees or annual revenue of 10 million euros or more in one of the 18 sectors. Affiliated companies are counted together.
What are some special cases?
Some organizations fall under NIS2 regardless of their size. These include:
- Operators of Critical Infrastructure (KRITIS)
- qualified trust service providers
- Top-Level Domain Registries
- DNS service provider
KRITIS operators are always considered critical infrastructure entities and have additional obligations.
What does NIS2 mean for SMEs and small and medium-sized businesses?
NIS2 specifically holds small and medium-sized enterprises accountable. A machinery manufacturer with 60 employees or a food producer with 12 million euros in revenue can already be considered a key facility. Although small businesses below the thresholds are not directly covered, they are often involved through the supply chain.
For an initial assessment, the BSI offers a free NIS2 impact assessment. While it does not replace a legal assessment, it quickly shows whether action is needed. Be sure to document the results in any case, even if you are not affected.
Are suppliers and service providers indirectly affected?
Yes, and more often than many people realize. Companies subject to NIS2 must manage and demonstrate the security of their supply chain. So they pass these requirements on to their suppliers through contracts, requests for proposals, security questionnaires, and documentation requirements.
Providers that are deeply integrated into their customers' systems are particularly affected:
- IT Service Providers and Managed Service Providers
- Cloud, SaaS, and hosting providers
- Software Supplier
- Maintenance and remote access service providers, such as those for production facilities
- Logistics and Platform Partners
For these companies, NIS2 is not considered a law but rather a contractual requirement. Those who cannot provide typical evidence of MFA, patch management, or incident reporting risk losing contracts in cases of doubt. Conversely, a verifiable level of security becomes a competitive advantage in bidding processes.
What requirements does NIS2 impose on companies?
Under Section 30 of the BSIG, affected companies must take appropriate, proportionate, and effective measures to protect their IT systems.
The law specifies ten minimum areas for this purpose:
- Risk Analysis and Safety Concepts
- Handling Security Incidents
- Business continuity—including backups, disaster recovery, and crisis management
- Supply Chain Security
- Security in the procurement, development, and maintenance of IT systems, including vulnerability management
- Assessment of the Effectiveness of the Measures
- Cyber Hygiene and Training
- Cryptography and Encryption
- Personnel Security, Access Control, and Asset Management
- Multi-factor authentication and secure communication
For certain digital providers—such as cloud services, data centers, and managed service providers—EU Implementing Regulation 2024/2690 specifies these measures in detail. It also serves as a good benchmark for all other companies regarding how closely auditors scrutinize their operations.
What do these measures mean in practice?
The easiest way to understand the catalog is as a cycle consisting of four phases:
- Prevention: Assess risks early and secure access points—especially admin accounts and remote access—using MFA.
- Detect: Log security-related activities and quickly address vulnerabilities.
- Respond: Establish a well-coordinated incident response process with clearly defined roles and 24/7 availability.
- Recovery: Test backups and recovery plans regularly to ensure that an incident does not result in a prolonged outage.
The NIS-2 Directive is not a project with an end date. Measures must not only exist on paper but must also be demonstrably effective, for example through recovery tests and incident drills.
What does NIS2 require of the supply chain?
NIS2 makes supply chain security a mandatory requirement, on par with backups and incident response. The reason is obvious: A compromised IT service provider with admin access can affect dozens of customers at once. Attacks via service providers and tampered software updates are therefore among the greatest threats to businesses.
How far does the supply chain responsibility extend?
The law focuses on relationships with direct suppliers and service providers. Companies must therefore primarily assess their direct contractual partners, not the entire chain all the way down to the last subcontractor. In this respect, NIS2 differs from the Supply Chain Due Diligence Act (LkSG), which also includes indirect suppliers.
Indirectly, however, this obligation extends further. If your cloud provider, in turn, uses subcontractors, you should know who they are. Otherwise, you cannot realistically assess the risk posed by your direct partner.
NIS2 primarily requires companies to manage their direct service providers. However, responsibility for incidents in the supply chain cannot be outsourced.
Who qualifies as a supplier under NIS2?
This refers less to traditional suppliers of goods and more to providers that have an impact on your IT and OT systems. Typical examples include:
- Cloud and SaaS Providers
- Data Centers and Hosting Providers
- Managed Service Providers and Managed Security Service Providers
- Software Supplier
- Remote Maintenance and OT Service Providers
- Providers of email, ERP, and identity services
What matters most in the evaluation?
The NIS2 Directive lists three criteria for evaluating direct service providers:
- their specific vulnerabilities
- the overall quality of their products and safety practices
- their development processes, such as in software
In addition, there are coordinated EU risk assessments for particularly critical supply chains, such as those for 5G components.
One key principle to keep in mind is this: The responsibility remains with you. Even if the cause of an incident lies with the provider, you are still required to report it. Supply chain security is therefore not solely an IT task; it affects procurement, the legal department, and supplier management equally.
NIS2-compliant supplier management is not a one-time project, but a cycle:
How do you implement NIS2 in supplier management?
Create a list of all providers related to your IT and OT systems. Document what services each provider offers and which systems and data they affect.
Ask whether the provider has access to internal systems, whether it operates business-critical platforms, and whether its failure would significantly disrupt your operations. A single point of failure with no alternative is always critical.
For critical vendors, establish a security baseline in the contract.
Re-evaluate critical vendors on a regular basis and as needed, such as when bringing in new subcontractors or making changes to services.
Determine how information will flow in an emergency, and practice the procedure with your key providers.
What contract clauses do you need?
The most important clause concerns the obligation to report incidents. Your service provider must notify you within a few hours and be available around the clock. Without this rule, you would have a hard time meeting your own 24-hour reporting deadline.
In addition, contracts with critical suppliers should address the following points:
- Access Protection: MFA and logged, time-limited admin privileges
- Vulnerability Management: Fixed Deadlines for Resolving Critical Security Vulnerabilities
- Business Continuity: Backup Strategies and Mandatory Recovery Objectives
- Subcontractors: Disclosure and Consent in the Event of a Change
- Documentation and Audit Rights: Certificates, Test Reports, and the Right to Conduct One's Own Audits
- Exit Policy: An Orderly Handover to Ensure That a Change in Provider Does Not Result in a Service Outage
The most important contractual provision is the service provider's obligation to report incidents. Without it, it would be nearly impossible to meet the 24-hour deadline set by the BSI.
What should be included in a NIS2 supplier questionnaire?
A good questionnaire asks not only about policies, but also about supporting documentation. Questions on these topics have proven effective:
- Existing certifications and their scope
- Use of MFA for Administrative and Remote Access
- Average time to patch critical vulnerabilities
- Date and result of the last restore test
- subcontractors used
- Security Incidents Over the Past Twelve Months
A few key performance indicators—which are nonetheless meaningful—are suitable for day-to-day management:
- Compliance with the agreed-upon patch deadlines
- Response Time for Incidents
- Results of Restore Tests and Emergency Drills
- Number of Outstanding Findings from Audits
Case Study: A Machinery Manufacturer and Its Maintenance Partner
A mechanical engineering company with 180 employees is registered with the BSI as a critical infrastructure entity. An external service provider maintains the production control system remotely, and accounting is handled in a cloud-based ERP system. The company classifies both providers as critical: one because of its privileged access, and the other because without it, neither orders can be placed nor deliveries made.
In supplementary agreements, the company MFA stipulates that remote access is permitted only upon authorization, requires an obligation to report incidents within four hours, and provides a 24/7 hotline. Months later, the maintenance service provider detects an attack on its own network and reports it that same evening. The machine manufacturer blocks access as a precaution and issues an early warning to the BSI within 24 hours. Without the contractual clause, it would not have learned of the incident until days later.
What reporting requirements apply under NIS2?
Significant security incidents must be reported to the BSI in three stages, in accordance with Section 32 of the BSIG. The clock starts ticking as soon as you become aware of a significant incident, not only once all details have been clarified.
An incident is considered significant if it seriously disrupts operations, causes major financial losses, or could cause significant harm to third parties. This also applies if the damage is merely imminent.
The Three Reporting Levels
They are assessing whether the incident could be the result of an attack and whether it has repercussions beyond Germany.
They update the early warning and assess the severity and impact, including, when possible, technical details such as suspicious IP addresses or domains.
Describe the cause, the nature of the threat, and the measures taken. If the incident is still ongoing, submit a progress report first.
The 24-hour deadline begins when the incident is reported. Without a well-established reporting process and 24/7 availability, it is virtually impossible to meet this deadline in practice.
Why do companies so often fail to meet the 24-hour deadline?
The phased approach requires a reliable initial assessment very early on. This requires close collaboration among IT security, senior management, communications, legal, and data protection teams. Often, especially in the early stages, information is lacking from the service provider where the incident originated. A tested reporting process with templates and on-call support is therefore one of the top priorities.
The BSI may also require you to notify your customers of an incident if your services could be affected, including, if necessary, by posting a notice on your website.
How does NIS2 registration work?
Affected companies must register with the BSI within three months, in accordance with Section 33 of the BSIG. For all those who were already affected when the law took effect, this deadline expired on March 6, 2026. The BSI accepted late registrations until July 31, 2026. By the end of May 2026, only about 18,500 of the approximately 29,500 affected organizations had completed their registration.
However, the deadline is not a one-time date. Anyone who becomes subject to the requirements later—for example, because the company exceeds the thresholds—must also register within three months.
Here's how registration works
Registration consists of four steps:
- Apply for an ELSTER organizational certificate: Access to the BSI portal is available exclusively through “My Business Account.” It takes a few business days to issue the certificate.
- Clarify sector allocation: When there are multiple business areas, this is often less clear-cut than expected. Clarify and document it in advance.
- Register on the BSI portal: You will provide your name, legal form, address, and contact information, as well as your public IP address ranges, your sector, and the EU countries in which you operate.
- Designate a point of contact: The BSI will reach you through this person in an emergency.
If your information changes, you must update it within two weeks at the latest. Registration itself is free.
NIS2 Deadline Missed: What Now?
Complete the registration as soon as possible. Failure to register constitutes a separate offense subject to a fine, and the BSI has announced that it will actively monitor compliance. Completing the registration along with a documented implementation plan will significantly improve your standing with the regulatory authority.
The registration deadline has passed, but the obligation remains in effect. Reporting and security obligations apply regardless of whether you are already registered.
Are members of management personally liable for NIS2?
Yes. Section 38 of the BSIG makes cybersecurity a top priority—and does so in a legally binding manner. Management has three obligations:
- Implementation: It must approve and implement the risk management measures.
- Monitor: She must check whether the measures are effective.
- Schools: She must regularly attend training sessions and be able to provide proof of attendance.
This responsibility cannot be delegated to the IT department.
If management culpably violates these duties, it is liable in accordance with the rules governing its legal form—for example, under Section 43 of the German Limited Liability Companies Act (GmbHG) for a GmbH, and under Section 93 of the German Stock Corporation Act (AktG) for an AG. This applies to all persons appointed to manage the business, namely managing directors, members of the executive board, and managing partners.
A cyber incident alone does not constitute grounds for liability. The decisive factor is whether management can demonstrate that it has fulfilled its organizational and monitoring obligations.
When does the situation become critical for managing directors?
Typical liability risks arise when there is no documented risk management system in place, when training cannot be verified, or when known vulnerabilities have been ignored. A lack of oversight of critical service providers can also become a problem.
Managers should therefore do four things right now:
- Personally approve and document risk management plans
- Allocate a binding budget and staffing for information security
- receive regular reports on the security situation, incidents, and supplier risks
- Plan, complete, and document your own training
What fines can be imposed for NIS2 violations?
Under Section 65 of the BSIG, particularly important entities face fines of up to 10 million euros or 2 percent of their global annual revenue. For important entities, the limit is 7 million euros or 1.4 percent. The higher of the two amounts applies in each case. If orders issued by the BSI are not complied with, additional penalty payments may be imposed.
How does the BSI conduct its audits?
The intensity of the BSI’s inspections depends on the category. For particularly important facilities, it may order audits and inspections even without a specific cause. For important facilities, it generally takes action only when there are indications of violations. Operators of critical facilities must also regularly provide evidence of the measures they have taken.
What are the risks in practice?
Violations of the basic principles are more likely to result in fines than violations involving the maximum penalty amounts. Auditors start by looking at areas where errors can be easily proven:
- Failure to register: often because the severity of the situation was misjudged
- Delayed reports: due to internal coordination or missing information from the service provider
- Paperwork Compliance: Guidelines Exist, but Testing and Documentation Are Lacking
- Unmanaged supply chain: no list of critical service providers, no contract clauses, no documentation
Audits are rarely about specific tools. Auditors want to see that security is managed and documented: in risk management, in reporting capabilities, in the supply chain, and at the executive level.
How does NIS2 relate to other regulatory frameworks?
NIS2 is not the only regulation. Many companies are subject to other requirements at the same time, some of which overlap and others of which complement each other. Considering them together helps avoid duplicating efforts.
NIS2 and ISO 27001
The list of measures in Section 30 of the BSIG is clearly based on ISO 27001. Therefore, organizations that already operate an information security management system in accordance with this standard have a strong foundation. However, certification is neither required for NIS2 nor does it automatically serve as proof of compliance. ISO 27001 does not cover registration, reporting procedures, and the obligations of management; you must specifically address these gaps.
ISO 27001 provides a good foundation for NIS2, but it is not sufficient on its own. Registration, reporting requirements, and management responsibilities are additional requirements.
NIS2 and GDPR
A cyber incident is not automatically a data breach, but it can be one. If personal data is involved, you must also notify the data protection authority within 72 hours. Both reports should therefore be based on a shared assessment of the situation to ensure that the information provided is consistent.
NIS2 and the Cyber Resilience Act
The Cyber Resilience Act (CRA) regulates the security of products with digital elements, namely software and connected hardware. Starting September 11, 2026, manufacturers must report actively exploited vulnerabilities; the remaining obligations will take effect in December 2027. This is important for the supply chain: Customers subject to NIS2 requirements will be able to use their software suppliers’ compliance with CRA obligations as a factor in their own supplier evaluations going forward.
NIS2 and the KRITIS Framework Act
The KRITIS Framework Act has been in effect since March 17, 2026. It supplements the IT security obligations under the BSIG by requiring the physical protection of critical infrastructure, for example against sabotage or natural hazards. Operators of critical infrastructure must consider both sets of regulations together.
NIS2 and LkSG
Organizations that have already established a supplier management system in accordance with the LkSG can build on that foundation. Risk analysis, supplier questionnaires, contract clauses, and event-driven audits follow similar methodological approaches. The difference lies in the subject matter: The LkSG protects human rights and the environment, while NIS2 protects cybersecurity. You can read more about due diligence obligations in our overview of the LkSG requirements.
Incidentally, special rules apply to financial institutions: For them, the Digital Operational Resilience Act (DORA) takes precedence over key NIS2 obligations.
In practice, we encounter the same mistakes time and again:
What obstacles should you be aware of?
Affiliated companies are included in the size assessment. Therefore, even a small IT subsidiary may be subject to NIS2.
Activities that are negligible in relation to the overall scope of work may be disregarded. However, this assessment must be clearly documented.
Companies that hire new employees or increase revenue may exceed these thresholds later on. Therefore, this issue should be addressed in an annual review.
Filling out a questionnaire just once is not enough. Auditors expect regular reassessments of critical service providers.
If services are outsourced to other providers, a lack of transparency creates a blind spot in risk management.
A security questionnaire, once completed, is no substitute for supplier management. NIS2 requires ongoing review of critical service providers.
Conclusion
NIS2 makes cybersecurity a legal requirement for approximately 29,500 companies and a contractual requirement for many more. The registration deadline has passed; the security and reporting requirements are in effect immediately, with no transition period, and company executives are personally liable. The greatest leverage lies in the supply chain: without reliable information from cloud providers, IT service providers, and maintenance partners, it is impossible to meet either the 24-hour deadline or to implement robust risk management.
Five questions to help you assess your NIS2 maturity level:
- Have you assessed and documented your exposure and registered with the BSI?
- Do you know which of your service providers have access to critical systems or constitute a single point of failure?
- Are security requirements and reporting obligations included in the contracts with these service providers?
- If a significant incident occurred today, would you be able to report it to the BSI within 24 hours?
- Can you demonstrate to an auditor that your measures are effective and that management is monitoring them?
If any of these questions remain unanswered, that’s no reason to panic—it’s simply a clear task to tackle. Most gaps can be closed with structured processes and thorough documentation.
FAQ
NIS2 is the EU Cybersecurity Directive (EU) 2022/2555. It requires critical and important facilities in 18 sectors to implement risk management, incident reporting, and registration. In Germany, it has been implemented since December 6, 2025, through the NIS2 Implementation Act within the BSIG.
The regulation applies to companies in 18 sectors that generally have at least 50 employees or annual revenue and total assets exceeding €10 million. Certain entities, such as KRITIS operators, DNS service providers, or qualified trust service providers, are covered regardless of their size. The BSI’s impact assessment provides an initial guide.
Directly, only if you fall into one of these sectors and meet the thresholds. Indirectly, this happens very frequently: Customers subject to NIS2 must secure their supply chain and therefore require proof of security, questionnaires, and contractual clauses from their IT service providers, cloud providers, and software vendors.
Companies must manage the security-related aspects of their relationships with their direct suppliers and service providers. In practice, this means identifying critical suppliers, establishing minimum requirements in contracts, obtaining supporting documentation, and conducting regular reviews.
Significant security incidents must be reported to the BSI in three stages: an early warning within 24 hours at the latest, a report within 72 hours, and a final report one month later. The deadline begins when the significant incident is first discovered.
Complete the registration immediately. The statutory deadline expired on March 6, 2026, and the BSI’s grace period ended on July 31, 2026. Failure to register may result in a fine; registering retroactively with an implementation plan will improve your position.
Yes. Under Section 38 of the BSIG, management must implement and monitor risk management measures. In the event of a culpable breach of duty, management is liable in accordance with the rules governing its legal form, such as Section 43 of the GmbHG. In addition, there is a training requirement.
No, but it provides a solid foundation. ISO 27001 covers a large portion of the measures required under Section 30 of the BSIG. You must also comply with the registration requirements, the tiered reporting procedure, and the obligations of management.
Critically important entities risk fines of up to €10 million or 2% of their global annual revenue; important entities risk fines of up to €7 million or 1.4%. In each case, the higher amount applies.
Larissa Ragg
LinkedInMarketing Managerin · lawcode GmbH
Larissa Ragg verantwortet die Content-Strategie bei lawcode und erstellt Fachbeiträge zu den Themen EUDR, ESG-Compliance, HinSchG, Supply Chain und CSRD. Ihre Beiträge auf dem lawcode Blog machen komplexe regulatorische Anforderungen verständlich und liefern Unternehmen praxisnahe Orientierung.